
Certfirst
CertFirst, a global integrated knowledge solution company has partnered with leading vendors to provide high quality and effective professional training solutions in the several areas of critical importance to enterprises including Project Management, Open Source, Software and Application Development, Information Security including Biometrics and others.
Cloud Cybersecurity
Topics Covered Why Cybersecurity CIA Triad NIST Cloud Computing Cloud Security Alliance Cloud Benefits Cloud Models Components of Cloud: Cloud Security Best Practices Firewalls Data in Transit Data at Rest Stateful vs. Stateless Firewalls Intrusion Detection Systems (IDS) Intrusion Prevention Systems (IPS) Next Gen Firewalls Unified Threat Monitoring Vulnerability Scanning Penetration Test in the Cloud Networking Engineering Amazon Web Services Security Azure Security Google Cloud …
$249.00
Fedramp System Security Plan (SSP) Control
Topics Covered What documents are required for initial package submission Why the SSP is one of the essential documents in the Security Package How to properly prepare for writing a SSP and submitting a Security Package How the SSP has organized an its relation to other documents included in the Security Package How to develop clear, concise, consistent, and complete information within each section of …
$249.00
Fedramp Continuous Monitoring Strategy
Topics Covered Roles and Responsibilities within the ConMon Process Expectation for monthly reports all the vulnerabilities within the Plan of Action and Milestones (POA&M) Impact of changes to the cloud service and how to properly address planned and unplanned changes What FedRAMP is looking for when a CSP delivers monthly authenticated scans Tips to Enable Successful and Effective ConMon strategies
$249.00
Fedramp Security Assessment Plan
Topics Covered What is a Security Assessment Plan? Laws, Regulations, Standards, Guidance Applicable Standards to FedRAMP FedRAMP Conops replaced by SAF Authorities for SAF 3PAO Accreditation Standards 3PAO Obligations FedRAMP Security Test Case Workbook Penetration Testing Plan and Methodology 3PAO Supplied Deliverables Penetration Test Rules of Engagement
$249.00
Fedramp Best Practices
Topics Covered FedRAMP process/flowchart Preparation/Authorization/Continuous Monitoring Selecting a FedRAMP 3PAO How to Become a 3PAO/Guidelines Security Testing SAP Template Security Test Procedure Workbooks SAR Template Running Scans Guidelines for CSPS Summary
$249.00
Internet of Things
Topics Covered What is the Internet of Things? How loT relates to IOT, Cloud and Big Data loT devices Smart home, Smart cars Home appliances Medical Devices Drones Industrial Control Systems (ICS) SCADA Systems – RTUs, PLCs Wearables loT Protocols lot Tools OWASP IOT Top 10
$249.00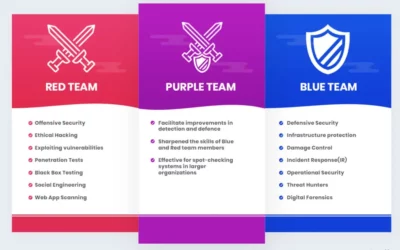
Purple Team (Red Team Interface with Blue Team)
Topics Covered Introduction to Purple Team Why is purple teaming important? Traditional Approach Purple Teaming Conducting A Purple Teaming Exercise What Does A Purple Team Do? When Does An Organization Need A Purple Team?
$249.00
Red Team Report Writing (Remediation/Action Plan)
Topics Covered Introduction to Report Writing Technical Writing Knowing your Audience Types of Reports Controlling Access to Reports Working with Various teams on reports Report Generation Tools Report Template
$249.00
Social Engineering
Topics Covered What is Social Engineering How does Social Engineering Types of Social Engineering Examples of Social Engineering Preventing Social Engineering ❖ Social Engineering Tools
$249.00
Physical Security Penetration Testing
Topics Covered Physical Security Penetration Testing Reconnaissance in Physical Security Types of Physical Security Controls Lockpicking Door Bypass Under door technique Bump keys Rec sensor bypass Physical Implant- USB Rubber Ducky, Bash Bunny, Bad USB Prox Card Bypass
$249.00
Exploit Frameworks/Exploit Kits
Topics Covered Intro to Exploits Zero Day Exploit Vulnerabilities CVEs Vulnerabilities vs Exploits Gaining Access Maintaining Access Covering Tracks Intro to Exploit Tools Password Cracking
$249.00
Cloud Penetration Testing
Topics Covered What Is Cloud Pen Testing What is laas, SaaS, PaaS (Cloud Service Models) Vulnerability Management In Cloud Cloud Pen Testing Tools Penetration Testing In The Cloud: AWS → Penetration Testing In The Cloud: Google Cloud How To Cloud Platforms Get Compromised? Cloud Security Biometrics Security And Cloud
$249.00
Troubleshooting to resolve cloud-related issues.
Program Objectives Given A Scenario Use Troubleshooting Strategy To Resolve Cloud Issues. Given-A Scenario Troubleshoot Security Issues. Given a Scenario, Troubleshoot Deployment Issues. Given A Scenario Troubleshoot Connectivity Issues. Given A Scenario Troubleshoot Common Performance Issues. Troubleshoot Automation Orchestration Issues.
$249.00
Cloud operations and support
Program Objectives Given a scenario, configure logging, monitoring, and alerting to maintain operational status. Given a scenario, maintain efficient operation of a cloud environment. Given a scenario, optimize cloud environments. Given a scenario, apply proper automation and orchestration techniques. Given A Scenario Apply Appropriate Backup and Restore Operations. Given a Scenario, Perform Disaster Recovery Tasks
$249.00
Cloud Deployment
Program Objectives Given a scenario, integrate components into a cloud solution Given a scenario, provision storage in cloud environments. Given a scenario, deploy cloud networking solutions Given a scenario, configure the appropriate compute sizing for a deployment. Given a scenario, perform cloud migrations.
$249.00
Cloud Security
Program Objectives Given a scenario, configure identity and access management. Given a scenario, secure a network in a cloud environment Given a scenario, apply the appropriate OS and application security controls Given a scenario, apply data security and compliance controls in cloud environments. Given a scenario, implement measures to meet security requirements Explain the importance of incident response procedures.
$249.00
Cloud Architecture and Design
Program Objectives Compare and contrast the different types of cloud models Explain the factors that contribute to capacity planning Explain the importance of high availability and scaling in cloud environments Given a scenario, analyze the solution design in support of the business requirements.
$249.00
Web Application Penetration Testing
Topics Covered Intro to Web Applications OWASP Top 10 Why web application Pen tests are done? SDLC Web Servers Apache NGINX Installation of Web Server Enumerating services Web Application Penetration Testing Tools
$249.00
Shell Scripting / Programming Languages
Topics Covered Introduction to Shell Scripting Different types of shells Shell commands Important Linux Commands Text editors Bash Scripting Python Scripting Perl Scripting
$249.00
Reconnaissance (Information Gathering/Discovery)
Topics Covered What is Reconnaissance? What types of information? What is OSINT? Goals of the Reconnaissance Phase Tools Enumeration Website reconnaissance Packet crafting Defense detection Tokens Wardriving Network traffic Cloud asset discovery Third-party hosted services Detection avoidance
$249.00
Scoping and Rules of Engagement
Topics Covered Open Source Security Testing Methodology Manual (OSSTMM 3) Terms and Definitions Definition of Scope Definition of Rules of Engagement (ROE) How to properly Scope a Project Identify resources that are “in scope” Resources that are “out of scope” What happens if there’s a violation of ROE
$249.00
Governance, Risk, and Compliance
Program Objectives Compare and contrast various types of controls. Explain the importance of applicable regulations, standards, or frameworks that impact organizational security posture. Explain the importance of policies to organizational security. Summarize risk management processes and concepts Explain privacy and sensitive data concepts in relation to security.
$249.00
Operations and Incident Response
Program Objectives Given a scenario, use the appropriate tool to assess organizational security. Summarize the importance of policies, processes, and procedures for incident response. Given an incident, utilize appropriate data sources to support an investigation. Given an incident, apply mitigation techniques or controls to secure an environment. Explain the key aspects of digital forensics.
$249.00
Implementation
Program Objectives Given a scenario, implement secure protocols Given a scenario, implement host or application security solutions Given a scenario, implement secure network designs Given a scenario, install and configure wireless security settings. Given a scenario, implement secure mobile solutions Given a scenario, apply cybersecurity solutions to the cloud. Given a scenario, implement identity and account management controls. Given a scenario, implement authentication and authorization …
$249.00
Architecture and Design
Program Objectives Explain the importance of security concepts in an enterprise environment. Summarize virtualization and cloud computing concepts Summarize secure application development, deployment, and automation concepts. Summarize authentication and authorization design concepts Given a scenario, implement cybersecurity resilience. Explain the security implications of embedded and specialized systems Explain the importance of physical security controls. Summarize the basics of cryptographic concepts
$249.00
Threats, Attacks, and Vulnerabilities
Program Objectives Compare and contrast different types of social engineering techniques Given a scenario, analyze potential indicators to determine the type of attack. Given a scenario, analyze potential indicators associated with application attacks. Given a scenario, analyze potential indicators associated with network attacks. Explain different threat actors, vectors, and intelligence sources. Explain the security concerns associated with various types of vulnerabilities. Summarize the techniques used …
$249.00
Recruiting Red Team Members
Topics Covered Skills required Personality Traits Outsourcing vs Developing In-House Soft Skills Interpersonal Skills Project Management Project Phases Team Player * Leadership
$249.00
Legal/Regulatory Compliance
Topics Covered Identify Legal Requirements pertaining to Red Team Engagements Target of the Engagement (Target of Evaluations) How to deal with Sensitive Data Client blames pen tester for loss of data How to get permission in writing-statement of Intent Confidentiality/Non-Disclosure Agreements Federally Mandated Red Team reporting PCI, FERPA, HIPAA, HITEC, SOX, GLBA State Laws on Hacking Authorized Actions vs. Restricted Actions
$249.00
Red Team Methodology
Topics Covered Intro what is red team? Why do we need red team? What is penetration testing and how is it different? What organizations should use Red Teaming- What is a Red Team Exercise- Red Team Purpose of a Red Team Exercise? Red Team Use Cases/Misuse Cases? What kind of personnel should be on a Red Team Why is it called Red Team? Difference Between …
$249.00